A React code audit should help a CTO or Head of Product decide what to fix, what to leave alone and whether a larger change is justified. Start with the product problem—slow releases, unreliable journeys or a difficult handover—then agree what evidence the review must produce.
Agree the Audit Scope Before It Starts
Name the user journeys, repositories, environments and integrations included in the review. Ask which areas will be sampled and which will receive deeper inspection. A checkout, permissions boundary or data-heavy dashboard may need more attention than a low-risk information screen.
Provide setup instructions, architecture notes and anonymized examples of the reported problems.
Agree access through your normal security process; do not share production credentials in a project brief.
Identify the engineers who can explain constraints and validate findings.
Define exclusions, deliverables and the decision the audit should support.
If you need a team to investigate and implement the resulting fixes, see our React development services . For wider changes across the product and its integrations, our software modernization services describe a phased approach.
Core Components of a ReactJS Audit
A thorough ReactJS audit examines your codebase on multiple fronts. Here are the key areas most top providers cover:
Code Quality & Maintainability: Identify anti-patterns, duplicated logic and enforce consistent style ( common React anti-patterns guide ).
UI/UX Consistency: Validate component structure, naming conventions and styling adherence.
Performance Optimization: Spot unnecessary renders, heavy bundle sizes and slow data fetches ( analyzing bundle sizes with webpack-bundle-analyzer ).
Migration and Upgrades: Plan seamless moves between React versions or major library shifts. For insights on building scalable web apps, refer to our guide on Building Scalable Web Apps with Next.js .
Integration Review: Check how your React components interact with APIs, state managers and third-party services ( Redux integration patterns ).
Dedicated Expertise: Engage a team that can not only audit but also mentor your developers.
Component | Focus Points |
|---|---|
Code Quality & Maintainability | Identify anti-patterns, remove duplicated logic, enforce consistent code style. |
UI/UX Consistency | Validate component structure, naming conventions, and styling adherence. |
Performance Optimization | Spot unnecessary renders, reduce bundle sizes, optimize data fetching. |
Migration and Upgrades | Plan seamless React version upgrades or major library transitions. |
Integration Review | Assess API interactions, state management, and third-party service integration. |
Dedicated Expertise | Provide audit insights and mentor developers for ongoing improvements. |
Unique Challenges in Legacy React Codebases
Older projects often mix class components, deprecated lifecycle methods and outdated dependencies. When you upgrade:
Check compatibility and documented breaking changes for the exact React and library versions involved.
Trace state ownership, subscriptions and effect cleanup across the critical journeys.
Profile the actual bottlenecks before proposing memoization or replacing class components.
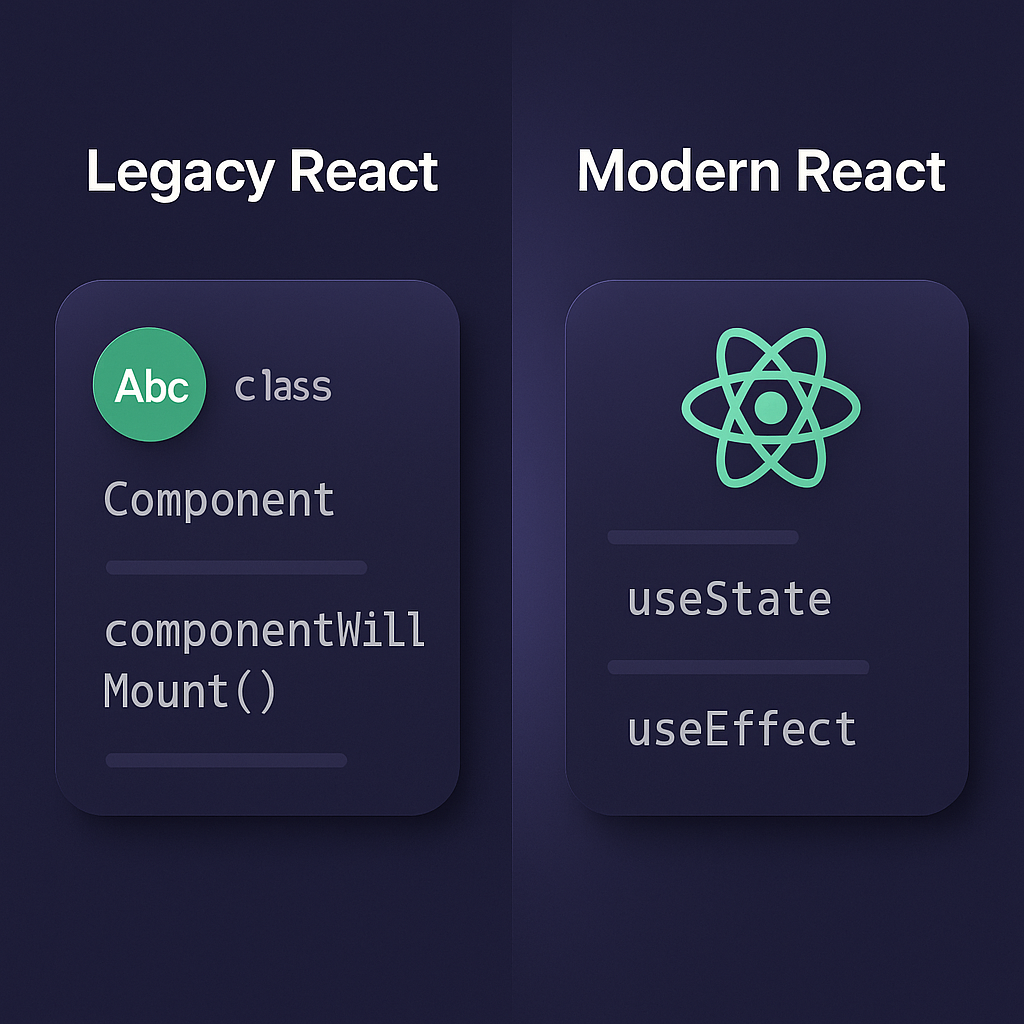
Impact of Version Upgrades on Audit Findings
Separate confirmed defects from upgrade risks and stylistic preferences. An old pattern is not automatically a production problem. For each proposed change, explain the affected behavior, the supporting evidence and how the fix will be verified.
Security-Focused Code Review Practices
React apps face the same threats as any web application—but plus a few of their own. When auditing for security, look for:
Raw HTML: React escapes ordinary text children, but dangerouslySetInnerHTML inserts raw HTML. Trace where that HTML comes from and how it is sanitized.
Dependencies: investigate relevant advisories and whether affected code is reachable, rather than treating a scanner count as the risk assessment.
Authorization and data handling: check API enforcement, session boundaries and what sensitive data reaches the browser. Hiding a button is not access control.
Use React’s dangerouslySetInnerHTML guidance as a starting point for raw-HTML review. A frontend code audit does not replace a dedicated penetration test or establish regulatory compliance.
Leveraging Automated Tools
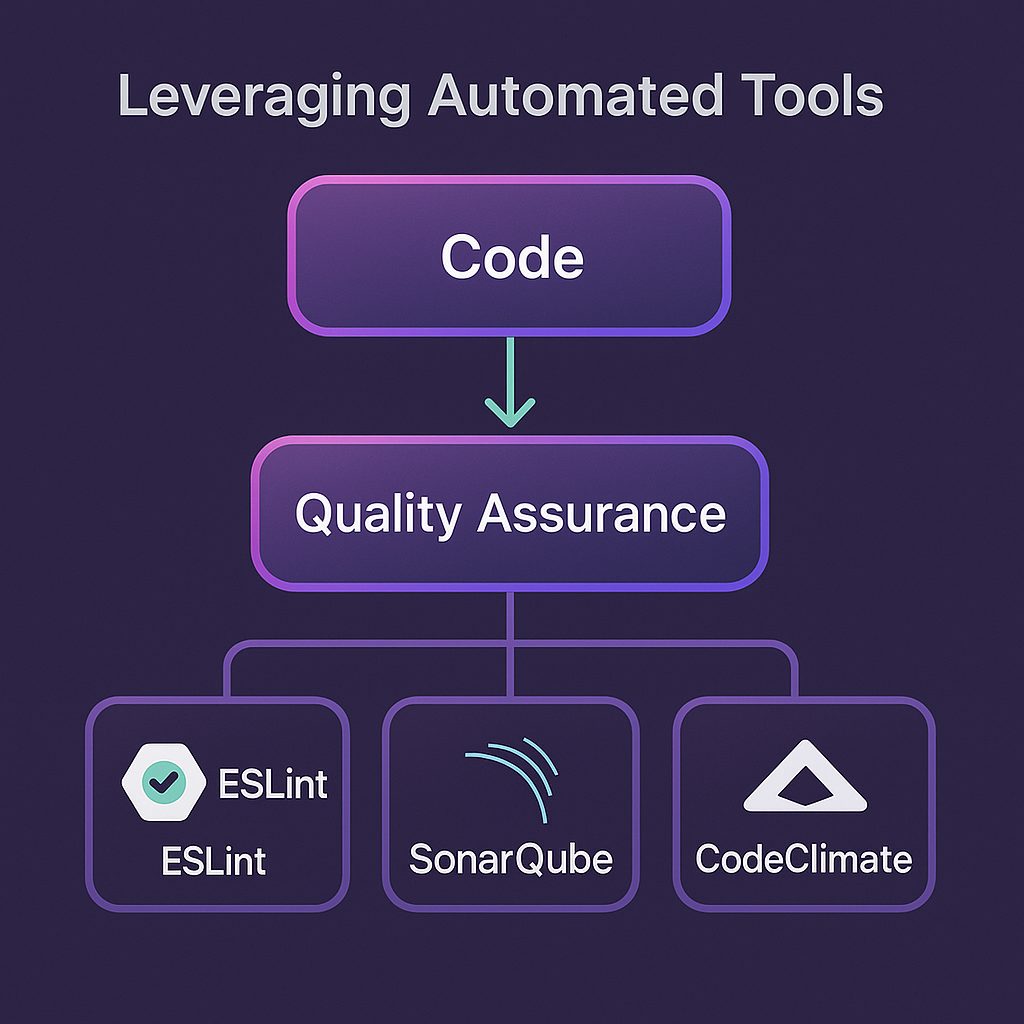
No manual review is complete without automation. Popular tools include:
ESLint: Enforce code style and catch common mistakes ( eslint.org ).
SonarQube: Give you a dashboard of code smells, bugs and vulnerabilities ( sonarqube.org ).
CodeClimate: Tracks maintainability over time and surfaces hotspots ( codeclimate.com ).
Interpreting Automated Findings
An exhaustive-deps warning can reveal stale closures or an Effect that needs restructuring. Do not suppress it simply to reduce renders. Use React’s dependency-rule guidance to identify the synchronization requirement and verify the fix.
Reviewing React Hooks and Custom Patterns
Hooks can simplify code but also mask complexity. During an audit, pay attention to:
Dependency Arrays: Incorrect arrays lead to stale state or infinite loops.
Custom Hook Side Effects: Hooks that fetch data or listen to events should clean up after themselves.
Reusability vs. Abstraction: Over-abstracted hooks can make the code harder to trace.
Pitfalls Often Missed
It’s common to see a custom hook that logs state changes but never removes its listener. A good audit flags these memory leaks and suggests patterns like returning a cleanup function.
Ensuring Accessibility in React Codebases
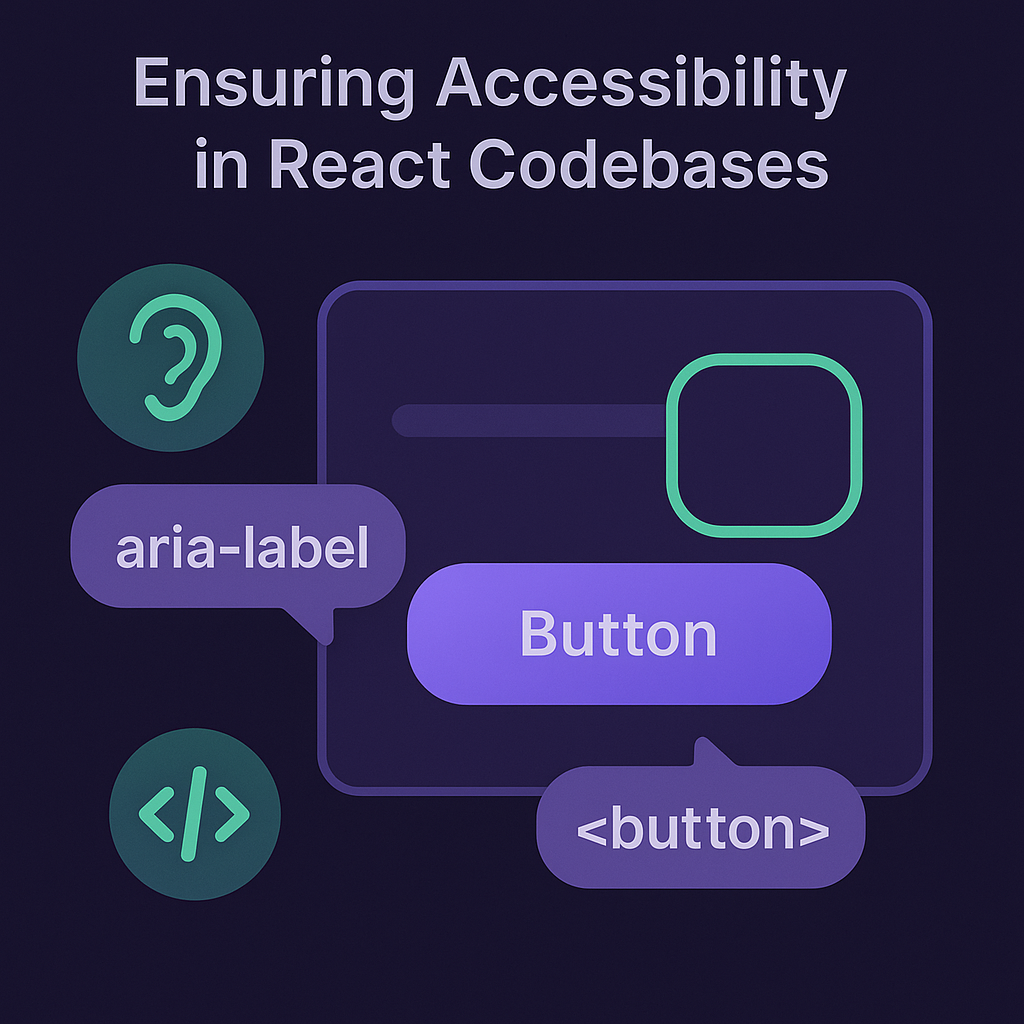
Accessibility (a11y) should be baked into your UI. During a code review, check for:
Correct use of ARIA attributes on interactive components ( WAI-ARIA 1.1 specification ).
Proper focus management when rendering modals or dynamic content ( keyboard accessibility techniques ).
Semantic HTML elements whenever possible (e.g.,
<button>instead of clickable<div>).
Tools and Techniques
Combine automated and manual tests:
axe-core for in-code or browser-based scans.
Keyboard-only navigation to verify focus order.
Screen reader walkthroughs with NVDA or Apple’s VoiceOver .
What a Useful React Audit Should Deliver
A short decision summary: the main risks, what can wait and whether a rewrite is justified.
A findings register with evidence, reproduction steps, affected journeys and confidence level.
A prioritized remediation plan showing dependencies, effort assumptions and verification criteria.
A handover discussion with the maintaining team, including unanswered questions and areas not tested.
Prioritize by Impact, Not by the Number of Warnings
Use a severity rubric agreed with the team. A credible route to unauthorized data access or failure of a critical workflow takes precedence over naming conventions. Separate severity from implementation effort so a small cleanup task does not displace a harder, necessary fix.
These are examples of report quality, not findings from a Makers’ Den client audit. Each real finding needs its own evidence and agreed acceptance criterion.
From Audit to an Implementable Plan
Group fixes into immediate risk reduction, improvements to the next delivery cycle and longer-term architectural work. Keep estimates conditional on access and scope; there is no useful universal audit price or duration for every React application.
Before engaging an external reviewer, ask who will do the work, how they reproduce findings, how your engineers participate and whether they can help implement fixes. Keep ownership of the repository, decisions and acceptance criteria with your team.
From Insight to Impact
Turn findings into work the product team can schedule. Address demonstrated risk first, verify improvements against the baseline and decide whether deeper modernization is warranted. The audit is useful when it changes a decision or prevents a recurring problem.
Discuss Your React Codebase
Tell us what is slowing delivery or creating risk. We can discuss the scope, constraints and useful next steps with your team.
Talk About Your React Project