HIPAA Compliance Checklist for Web Applications: Current Rules and Proposed Changes
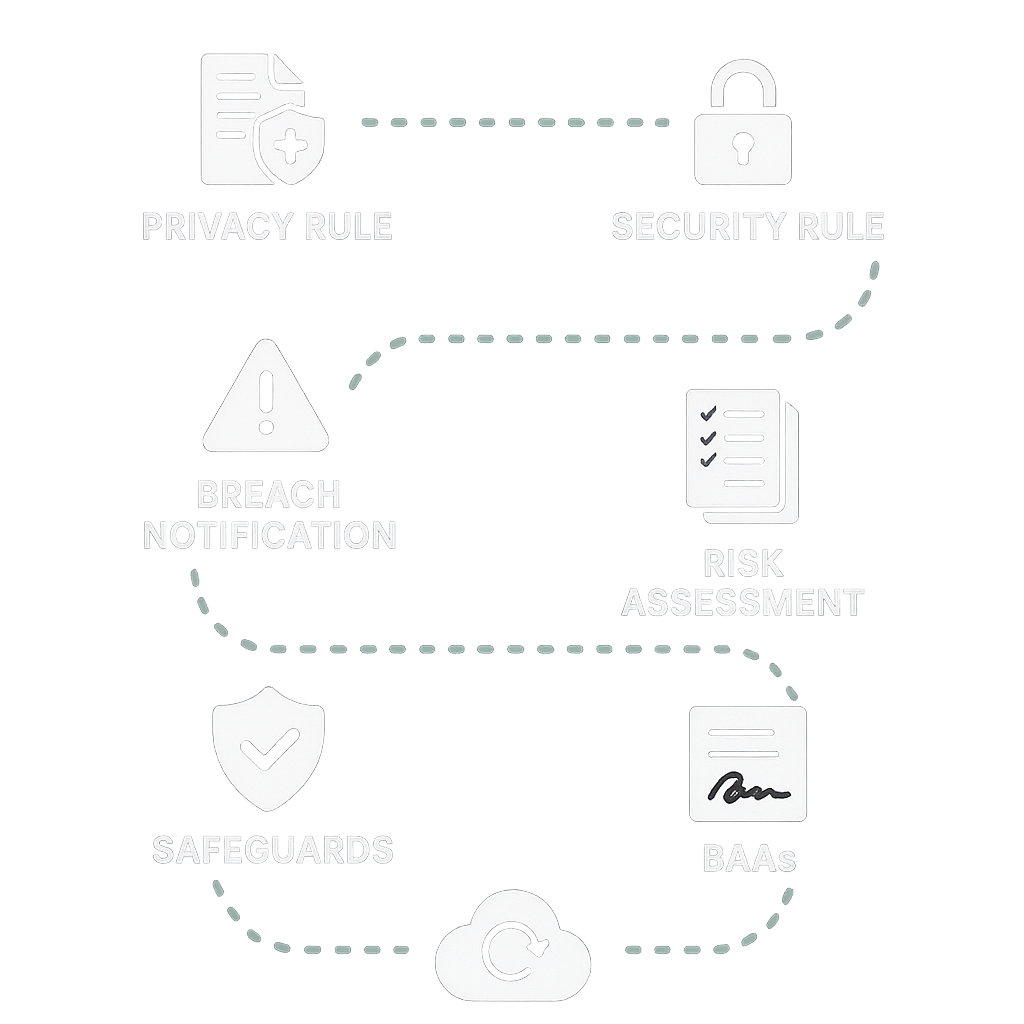
This guide maps HIPAA rules to practical web-app safeguards. The January 2025 Security Rule update is a proposal, not a current mandate. Assess controls such as multi-factor authentication and security testing against the rule in force and your documented risks.
Understanding the Three Core HIPAA Rules
Every HIPAA-covered entity and business associate must satisfy:
Rule Name | Description | Reference Link |
|---|---|---|
Privacy Rule | Governs uses and disclosures of PHI and patient rights | |
HIPAA Security Rule | Requires administrative, physical, and technical safeguards for ePHI | |
Breach Notification Rule | Individual notice without unreasonable delay and within 60 days; HHS and media obligations depend on breach size |
Privacy Rule: Governs uses and disclosures of protected health information (PHI) and grants patients rights over their PHI.
HIPAA Security Rule: Requires administrative, physical, and technical safeguards to ensure the confidentiality, integrity, and availability of electronic PHI (ePHI).
Breach Notification Rule: Notify affected individuals without unreasonable delay and no later than 60 calendar days after discovering a breach of unsecured PHI. For 500 or more affected individuals, notify HHS contemporaneously with individual notice; for fewer than 500, maintain a log and report to HHS within 60 days after the calendar year ends. Media notice applies when more than 500 residents of a state or jurisdiction are affected and is due without unreasonable delay and no later than 60 days after discovery, subject to applicable law-enforcement delay provisions.
Conducting a Thorough Risk Assessment
A risk assessment lays the foundation for all your security activities:
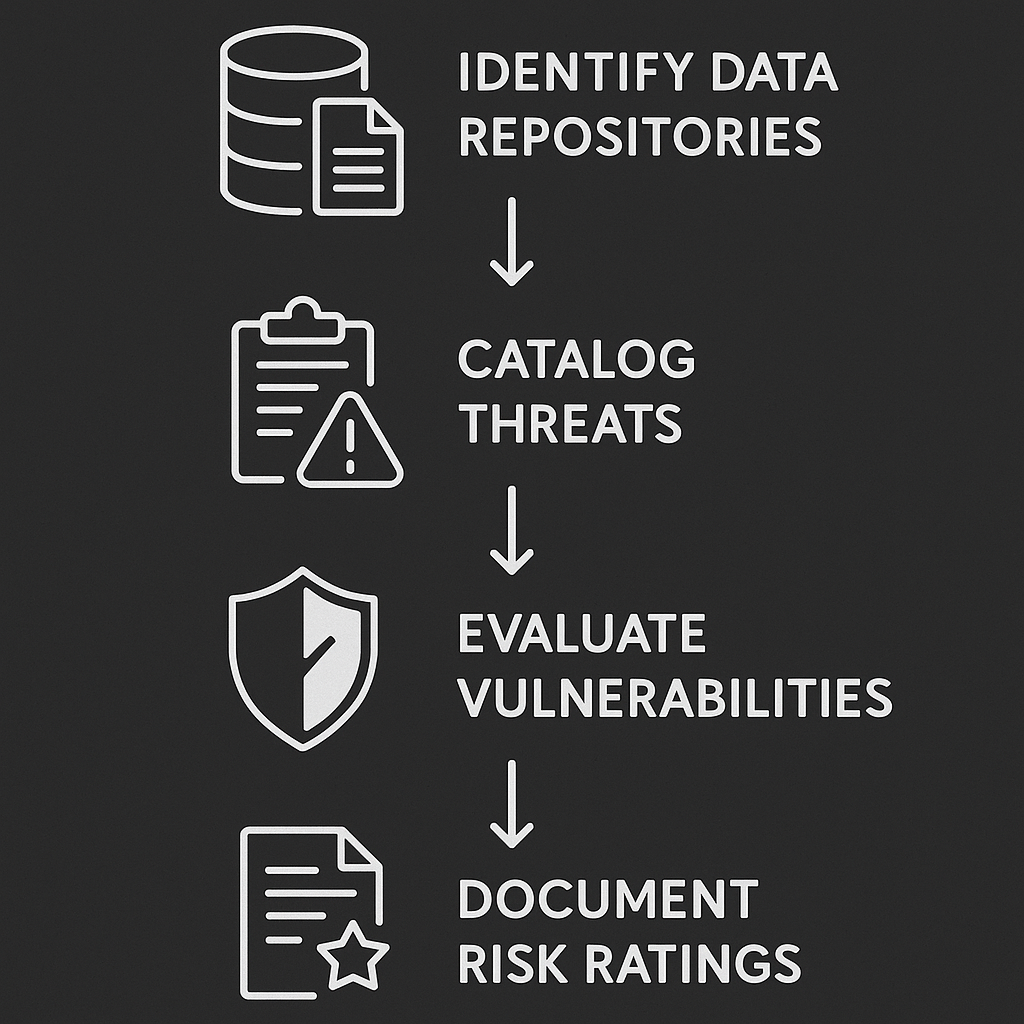
Identify ePHI repositories in your web app (databases, logs, backups).
Catalog threats (unauthorized access, injection attacks, data leaks).
Evaluate vulnerabilities and likelihood.
Document risk ratings, remediation timelines, and residual risk.
If your web app has a React frontend, a React code audit can help your team scope a review of authorization boundaries, browser data handling and reproducible code findings. Treat it as one input to your risk assessment, not as a penetration test or proof of HIPAA compliance.
Security Testing and Periodic Evaluation
The current HIPAA Security Rule calls for periodic technical and nontechnical evaluations, but it does not prescribe six-month vulnerability scans or annual penetration tests. Set your testing schedule from your risk analysis; for assessment methods, consult NIST Special Publication 800-115.
Establishing Strong Administrative Safeguards
Administrative controls set your governance framework:
Appoint a dedicated Security Officer and Privacy Officer.
Develop and publish policies & procedures covering access management, incident response, data retention, and third-party/vendor oversight.
Train your workforce on HIPAA basics, phishing awareness, and reporting protocols at hire and annually thereafter.
Review and update policies at least biannually or after any significant change.
Maintain a documented incident response plan that defines roles, communication channels, and breach reporting timelines.
Implementing Physical Safeguards
Protecting your servers, workstations, and data centers is critical:
Facility access controls (door locks, badge readers, visitor logs).
Device and media controls (asset tagging, secure disposal, encrypted portable media).
Environmental protections (surge suppressors, fire suppression systems, temperature/humidity monitoring).
Enforcing Technical Safeguards
Your technical controls directly protect ePHI in use, transit, and storage.
Safeguard Category | Key Measures |
|---|---|
Access Controls | Unique IDs, RBAC, MFA |
Audit Controls | System logging, anomaly detection, monthly reviews |
Integrity Controls | Checksums, digital signatures |
Transmission Security | TLS 1.2+, AES-256 at rest |
Access Controls
Use unique user IDs and role-based permissions. Consider multi-factor authentication for access to ePHI based on your risk analysis; the current Security Rule does not require MFA for every login. For digital-identity implementation details, consult NIST SP 800-63B guidelines for digital identity.
Audit Controls
Implement system activity logging, monitor for anomalies, and review logs monthly to detect unauthorized access or data exfiltration.
Integrity Controls
Use checksums or digital signatures to verify that ePHI hasn’t been tampered with.
Transmission Security
Encrypt all ePHI in transit (TLS 1.2+ with strong ciphers) and at rest (AES-256 or better).
Securing APIs for Interoperability
If your app uses FHIR APIs or participates in health information exchanges, conduct specialized security assessments that include schema-level validation, rate limiting, OAuth 2.0 scopes, and JSON schema fuzz testing, as recommended by HL7 FHIR Security Guidance.
Managing Business Associate Agreements (BAAs)
Any vendor with access to ePHI—cloud providers, third-party analytics, billing services—must sign a BAA that spells out permitted uses, security obligations, breach notification processes, and termination rights.
Ensuring Data Backup and Disaster Recovery
Regular backups and a tested recovery plan are non-negotiable:
Schedule daily encrypted backups of databases and critical logs.
Store backups off-site or in a separate cloud region.
Define and test recovery time objectives for systems handling ePHI based on your risk analysis and operational needs; the current HIPAA Security Rule does not prescribe a 72-hour RTO.
Asset Inventory & Network Mapping
Maintain a living inventory of all hardware, virtual machines, containers, medical devices, and network segments that store or transmit ePHI. Update it quarterly and use network diagrams to identify trust zones and firewall boundaries.
HIPAA vs SOC 2: Why You Might Need Both
HIPAA Security Rule is legally required for PHI; SOC 2 is a voluntary assurance framework for service organizations.
SOC 2’s Trust Services Criteria overlap with HIPAA’s safeguards (security, availability, confidentiality) but don’t address patient rights or breach notifications.
A SOC 2 Type II report can help demonstrate control effectiveness, but you still need HIPAA-specific policies and BAAs, as explained in this Crowe comparison of HIPAA vs SOC 2.
Your Next Steps on the Path to Compliance
You’ve covered the essentials—from understanding HIPAA’s three rules to implementing advanced controls like MFA, pen testing, FHIR API security, disaster recovery benchmarks, and asset inventories. Now, build your project plan and set calendar reminders for every assessment, training session, and policy review. By staying proactive, you’ll be well-positioned to protect patient data and satisfy auditors.