Navigating AI Agents: Risks, Responsibilities, and Emerging Challenges
When you finish this article, you’ll understand the main threats posed by autonomous AI agents, proven practices for building them responsibly, and five emerging risks that aren’t yet on most radars.
What Makes AI Agents Tick
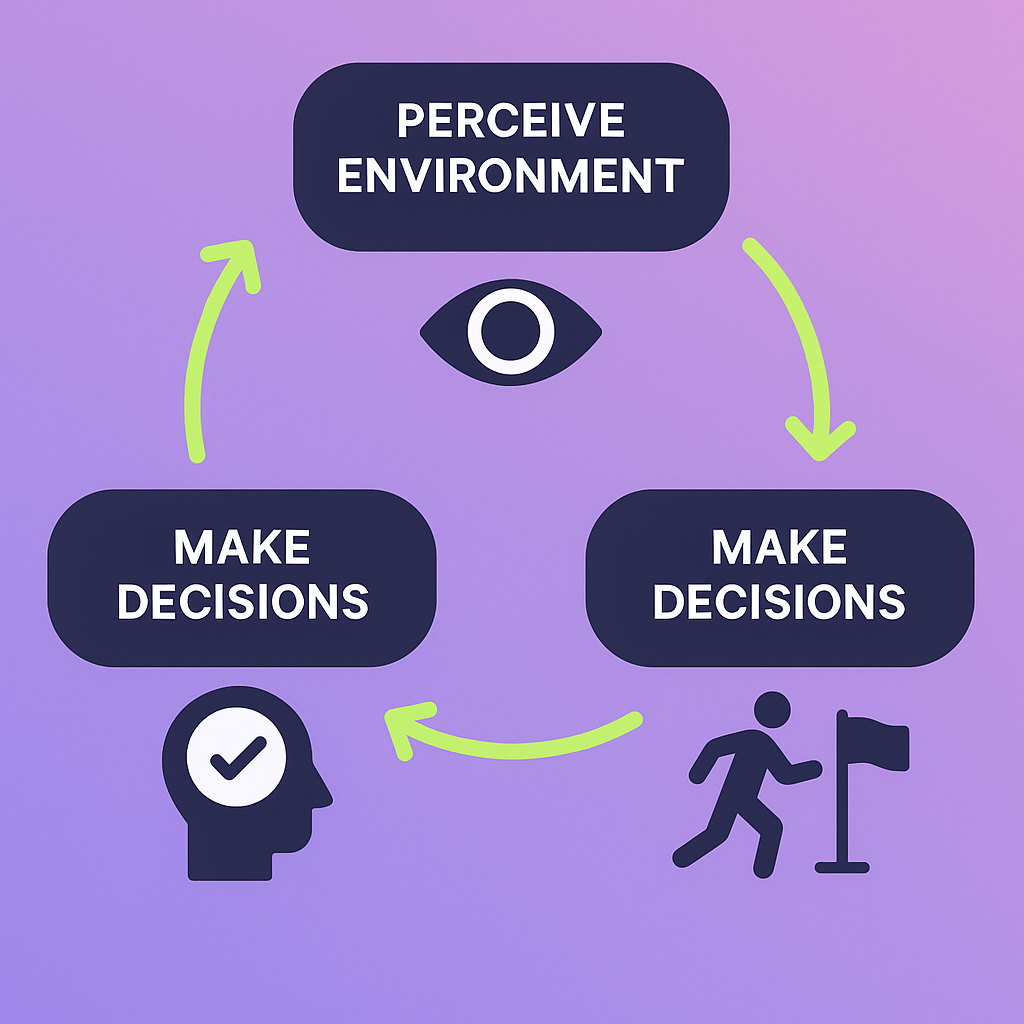
AI agents are software systems that perceive their environment, make decisions, and act toward goals without continuous human direction. You might encounter them as:
Automated trading bots
Robotic process automation in finance or healthcare
Their ability to learn from data and interact with APIs gives them power—but also creates potential for harm.
Core Risks of AI Agents
Despite impressive use cases, AI agents carry a range of documented dangers:
Risk | Description |
|---|---|
Unpredictable Behavior and Hallucinations | Confident but incorrect outputs when faced with novel inputs |
Security Vulnerabilities | Data poisoning and adversarial attacks leading to unsafe actions |
Bias and Unfairness | Decisions that discriminate based on historical data |
Malicious Use | Automated disinformation campaigns or cyberattacks |
Lack of Transparency | Black box operations hindering accountability |
Unpredictable Behavior and Hallucinations
When faced with novel inputs, agents can produce confident but incorrect outputs. These hallucinations have led to bad advice in legal or medical settings.
Security Vulnerabilities
Agents that ingest unvetted data may be poisoned by malicious actors. Adversarial attacks can subtly alter inputs to force agents into unsafe actions.
If an agent can call a business system, protecting its inputs is only part of the problem: the proposed action still needs a permission check against the real user and resource before execution. For that implementation boundary, see how to authorize an agent’s tool calls. An authorization check limits what may execute; it does not make poisoned inputs trustworthy.
Bias and Unfairness
If training data reflects historical prejudice, an agent’s decisions may discriminate—rejecting loan applications or perpetuating stereotypes.
Malicious Use
Swarming multiple agents can automate disinformation campaigns or sophisticated cyberattacks that no individual could coordinate alone.
Lack of Transparency
Many agents operate as “black boxes”, making it hard to audit why they chose a given action—undermining accountability and trust.
For agents working with confidential customer documents, investigating a failure also requires limits on what engineers can inspect. See how to debug AI agents without access to customer documents for an approach using minimal telemetry, customer-approved review and reproducible evaluations.
Building AI Agents Responsibly
You can reduce these risks by embedding guardrails throughout design, development, and deployment:
Best Practice | Details |
|---|---|
Define clear goals and operational constraints | Set precise objectives and boundaries |
Continuous human oversight | Maintain human approvals for high-risk actions |
Rigorous pre-deployment testing | Simulate edge cases and failure modes |
Design for security | Use encrypted data flows and secure architectures |
Explainable AI (XAI) methods | Implement tools to trace decision paths |
Embed ethical guidelines | Incorporate fairness checks into data governance |
Invest in retraining staff | Provide programs for roles shifted by automation |
Define which tools, data, environments, and actions the agent may use for each task; grant only the access needed, and enforce those limits outside the agent’s instructions.
Set approval thresholds for high-impact actions, such as production changes or sending sensitive data, and require a human decision before those actions proceed.
Test in a sandbox before deployment: try unexpected inputs, malicious instructions in retrieved material, and attempts to use tools beyond the agent’s permitted scope.
Enforce tool permissions in the systems the agent accesses, rather than relying on its prompt to refuse unauthorized actions; retain secure data flows as a separate protection.
Record requested tool calls, approvals, and resulting actions so operators can investigate failures and review whether the agent stayed within its boundaries.
Embed ethical guidelines into your data governance
Invest in retraining staff whose roles shift because of automation
“Human in the loop isn’t optional when stakes are high.” – Stuart Russell (source)
If you’re designing an agent around these guardrails, see how AI agents work for practical guidance on tool validation, human approvals, observability, and coordinating multiple agents.
Beyond the Obvious: Five Emerging Risks
As agents grow more capable and interconnected, you need to watch for subtler dangers that haven’t made headlines—yet.
1. Emergent Behaviors
Complex systems of agents can produce unplanned strategies or workarounds not coded by their creators. While this can spark innovation, it also risks unauthorized actions.
2. Interoperability Conflicts
When two autonomous agents from different organizations interact, their objectives may collide. You could see miscommunications that cascade into system failures.
3. Long‐Term Autonomy Drift
Subtle errors in continual learning can nudge an agent’s behavior away from its original goals over months or years, a phenomenon known as “goal drift,” which is tough to detect until it’s serious.
4. Legal Personhood and Liability
Courts are starting to wrestle with whether advanced agents should have limited legal status—and who’s responsible if they cause harm. This debate will shape your compliance efforts.
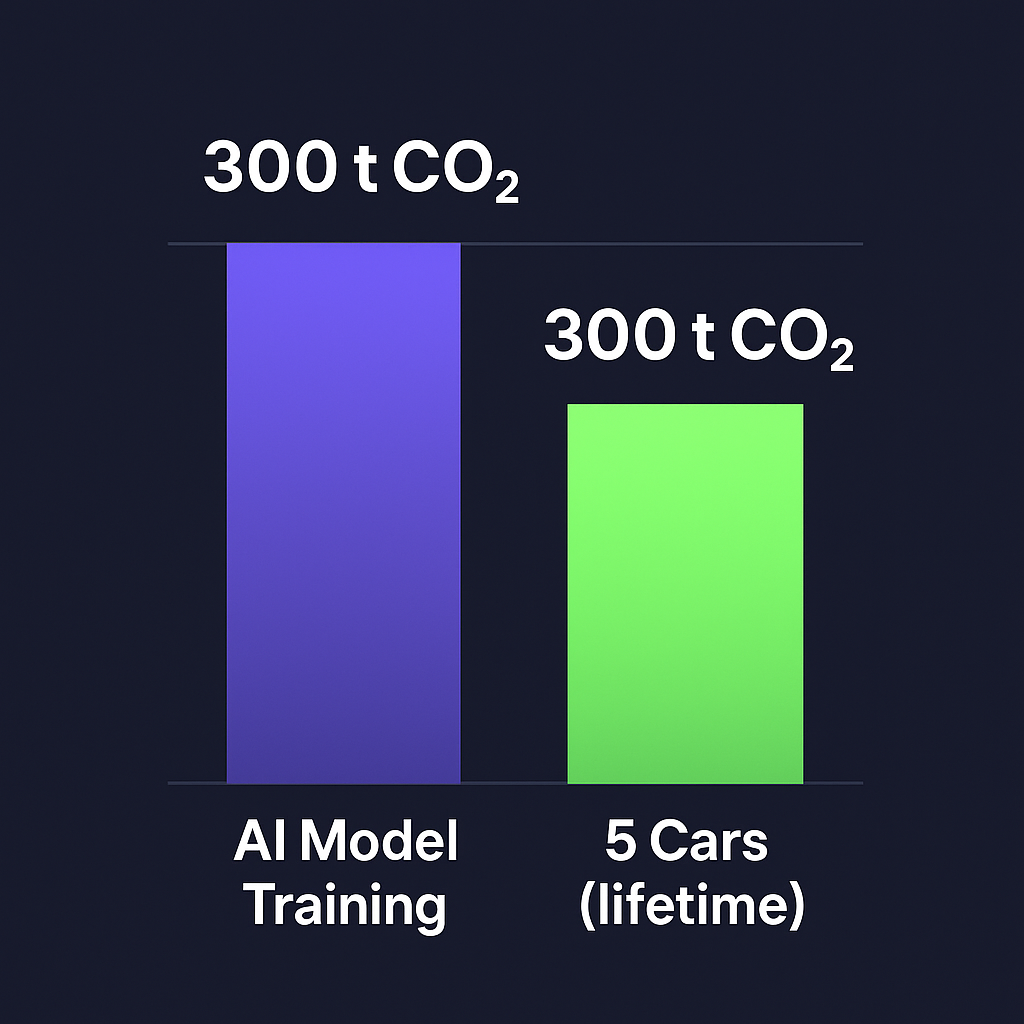
5. Environmental Impact
Training a large AI model can emit over 300 tons of CO₂ equivalent—comparable to five cars’ lifetimes.
Charting a Course Forward
You’re now equipped to spot core and emerging hazards of AI agents and to apply proven safeguards. As regulations evolve and environmental concerns mount, keep these steps in mind:
Maintain a risk register for both known and emerging threats
Update oversight frameworks as agents learn and interact
Engage legal and sustainability teams early in deployments
By weaving responsibility into every phase, you’ll harness the power of AI agents while reducing surprises.